Transaction monitoring for crypto firms: scenarios, thresholds and the handling of alerts
Published: Last reviewed: Editorial standards
Transaction monitoring is the practice of watching customer activity for patterns that may point to money laundering, fraud or sanctions risk, followed by review and a record of each alert. For a crypto business this covers on-chain transfers alongside bank and card payments. We coordinate independent specialists who assist with scenario design, threshold setting, tool selection and written alert procedures. Your compliance officer decides on alerts and reports, and no configuration detects every case.
Any question on your case may be put to us here:
Who this service is meant for
- An exchange, broker, payment or wallet business in crypto that began operating without formal monitoring in place
- A compliance officer facing a high volume of mostly false alerts and uncertain how to record the reasoning behind decisions
- A product team introducing staking, cards or cross-border transfers that alter existing activity patterns
- A team comparing monitoring tools that first wants its requirements set down in writing
- Founders who need to demonstrate to a bank or an auditor how suspicious activity is identified and addressed
The procedure for a case
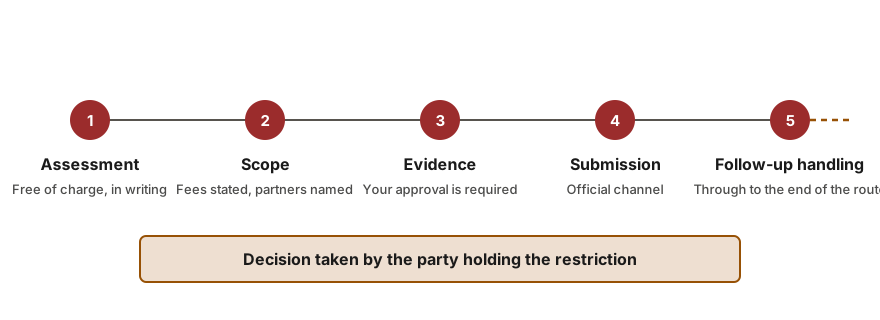
- Free initial assessment
You describe the business and its current monitoring procedure. We respond in writing with an assessment of whether independent specialists can assist and what records they would require.
- Scope and fee in writing
You will receive a formal written notice detailing the project scope, designated specialists, expected outcomes, and the fee structure before any payment is required before moving to the next phase.
- Data Review and Information Discovery
Independent specialists examine your transaction flows, written policies and a sample of closed alerts. They record where data is missing and identify the scenarios that merit construction.
- Design and testing
The specialists prepare draft scenarios, thresholds and written procedures, then run them against your own historical data. Our team sits down with yours to review the results and make adjustments.
- Handover and date of review
You are given the completed documentation, a training session for your personnel, and a scheduled date for the first review of alert outcomes after launch.
What to prepare
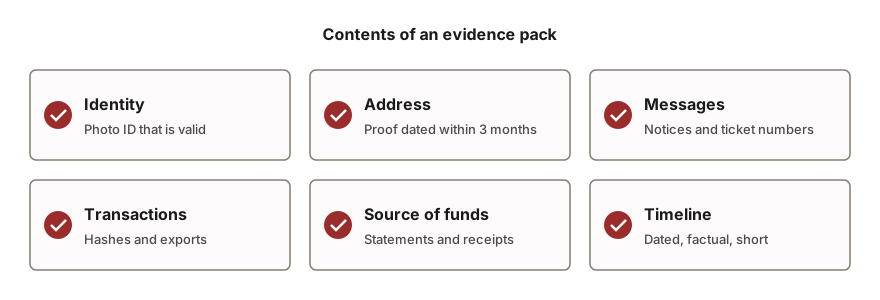
- An account of your products, customer categories, jurisdictions served and typical transaction values
- The monitoring rules, thresholds and tool configuration presently in use, where such records exist
- A sample of recent alerts together with the closure recorded for each, stripped of personal data
- Alert statistics, covering monthly volumes, the proportion closed without action, and the time taken to close
- Your AML policy document and the method used to assign customer risk ratings
- The screening, monitoring and analytics providers you already use or may adopt
- Questions or findings concerning monitoring, raised by a bank, an auditor or a regulator
What our work involves
- Determine Scope and Identify Relevant Risks
This procedure begins by analyzing the movement of capital and crypto assets within your business operations. It evaluates deposit routes, customer demographics, country of origin, and typical transaction values to distinguish substantial risk patterns from routine system noise.
- Set scenarios and thresholds
Specialists draft monitoring scenarios based on criteria such as rapid capital flow or links to high-risk countries. Initial thresholds and the basis for them are tested against account history before they are implemented.
- Assist in choosing and configuring monitoring tools
Assistance is available for drafting requirements for on-chain analytics, screening and case management tools, comparing available options and planning a trial. As part of this, we verify that the data such tools depend on, for example wallet addresses and travel rule fields, actually reaches them.
- Draft the alert handling procedure
A written procedure sets out who reviews each alert, which records the reviewer checks, how long a review may run, how the decision is documented, and at what point a case is referred to the compliance officer. Careful notes protect your staff and let a supervisor follow how each decision was reached.
- Adjust settings and review over time
Once the system is live, the specialists sit with you to examine alert outcomes, identify false positives and patterns that were not caught, and recommend adjustments. Every adjustment is recorded with its date and the reasoning behind it, so you maintain a written record of how the monitoring evolved.
What falls outside our role
- No monitoring setup detects all suspicious activity. We design systems for your defined risks, but we cannot promise that a specific scenario will identify a certain pattern.
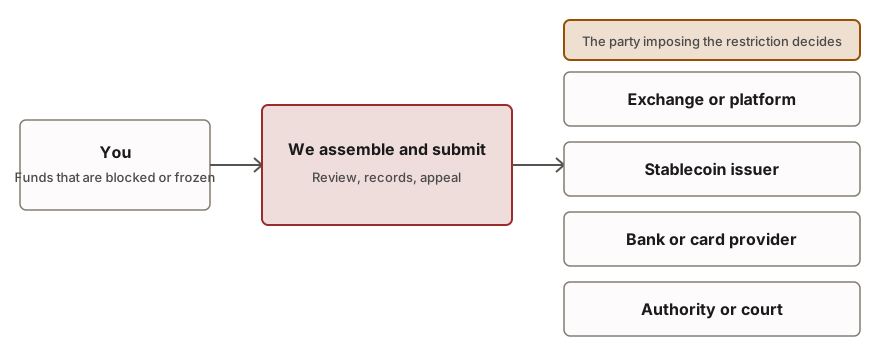
- Decisions on each alert and on any submission to an authority rest with your compliance officer. We do not examine live alerts, take those decisions or submit reports on your behalf.
- We provide no legal advice and are neither an auditor nor a licensed officer. We cannot require a supervisor or a bank to approve your system, and we cannot forecast its position.
- Recommendations on tools follow your stated requirements. The purchase and the contract remain your responsibility, and until a tool is tested we cannot state that it will perform with your data.
- Monitoring design is built on data and procedures, so we never request seed phrases, private keys or passwords, and we never handle customer funds.
Expected timeframes
An initial design for a small business may require several weeks, and tuning proceeds after go-live, since live alerts reveal gaps in the first thresholds. Phases and review dates are set in the written scope.
Fees
The assessment carries no charge. Following it, each phase is quoted in writing, with the independent specialists' fees listed separately, so you may halt after any phase. No fee is taken before we confirm whether we can assist. Fees →
Frequently raised questions
What does transaction monitoring mean?
In practice, this means the continuous examination of customer activity in order to identify unusual or suspicious patterns. Rules or models generate alerts, a member of staff examines each alert, records the decision in writing, and escalates where the procedure requires it. For crypto firms, the scope includes on-chain transfers alongside bank and card payments.
Does on-chain monitoring take the place of KYC?
It does not. KYC establishes the identity of the customer. Monitoring then observes what that customer does afterwards. On-chain screening contributes risk data about the wallets involved, but it cannot establish who controls a wallet or the reason behind a payment.
How can we bring down the number of false alerts?
As a rule, you begin with the purpose of each scenario, test thresholds against your own historical data, and combine related alerts into a single case. Rules that never produce an actionable response are removed, and the reason for removal is recorded. Reducing alerts without a structured basis can create real coverage gaps, so every change is tested and documented in writing.
Who makes the decision to report suspicious activity?
Your compliance officer, or whoever your internal policy designates for that role. The duty to report belongs to the regulated business itself, and the procedure differs between countries. We do not submit reports on your behalf. We can assist in drafting the internal procedure and the record of each decision.
What does the travel rule cover, and how does it connect to monitoring?
It is a rule, in force in certain jurisdictions, under which specified crypto businesses transmit sender and recipient information together with a transfer. That information can support monitoring, for instance by identifying the counterparty to a transfer. Whether the rule applies to your business depends on your jurisdiction and on the services you provide.
Could you operate monitoring on our behalf?
No. Our work does not include reviewing live alerts or serving as your compliance function. We assist with design of the system, selection of tools, drafting of written procedures, and training for your team. Day-to-day alert review, as a rule, remains with your own staff or with a provider you contract with directly.
Common situations
- No formal written regulations dictate specific activities that must trigger a formal alert.
- Monitoring tools operate upon default configurations, and the suitability of these established thresholds for your clients is unknown.
- The quantity of alerts often exceeds the capacity of the team, resulting in closures with minimal documentation.
- Deposits originating from wallets with indirect exposure are flagged, yet a standardized protocol for handling such events has not been established.
- An external authority or a chartered bank may observe deficiencies regarding the review and subsequent recording of issued alerts.
- The on-chain screening process must be linked with stated customer risk ratings and with relevant travel rule data.
- The introduction of a new market or product necessitates reevaluation, as previously defined scenarios are no longer appropriate.
Related situations
- AML Compliance Procedures for Cryptocurrency Entities. Specialists assist with the drafting or review of your AML policies and associated risk assessments.
- Crypto firm due diligence and risk reviews. Evidence-based, written checks on customers, counterparties and wallets, each with a documented risk rating.
- Disputing risk flags from wallet screening. High-risk address flag from screening tools: record the funds path and dispute it.
- Report on blockchain transaction analysis. A source-of-funds report based on transaction tracing, prepared in a form a compliance team can review.
Read next
Sources
Authoritative and official pages on which this page relies. Such pages are updated, so confirm the current wording at the source itself.
- Guidelines amending the ML/TF Risk Factors Guidelines (EBA/GL/2024/01) · European Banking Authority
- Guidelines on information requirements in relation to transfers of funds and certain crypto-assets transfers · European Banking Authority
- Application of FinCEN's Regulations to Certain Business Models Involving Convertible Virtual Currencies (FIN-2019-G001) · Financial Crimes Enforcement Network (FinCEN)
The content on this page is general in nature and is not legal advice.