Sharing documents with a recovery service safely: what to submit and what to withhold
Published: Last reviewed: Editorial standards
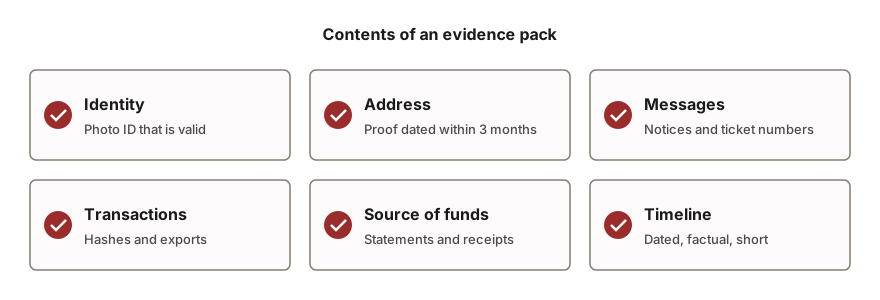
Initial disclosure should be phased to protect your interests throughout the entire process. For the initial review, providing a brief written summary along with public identifiers such as transaction hashes and wallet addresses is sufficient. Sensitive records and identity documentation must only be submitted after you have confirmed the identity of the recipient and established a documented scope. Never disclose a seed phrase, private key, password, or device remote access to any party, regardless of the request or stated reason.
Any question on your case may be put to us here:
Share information in stages, not everything at once
People who have lost crypto receive document requests from exchanges, banks, police, lawyers and recovery services. Fraudsters are aware of this. Certain fake services exist for the sole purpose of collecting identity papers, wallet access, or both.
A legitimate provider requires facts about what took place. It has no need for the secrets that control your wallet. When you share in stages and verify each party first, a real provider receives what it needs and a fake one receives almost nothing.
| Stage | What you may provide | Condition |
|---|---|---|
| 1. First Assessment | A concise written statement that includes the names of platforms, relevant dates, monetary figures, transaction identifiers, and the public addresses of your wallets. | This stage constitutes a preliminary verification that the involved party exists and generally does not require identity documentation at this specific time. |
| 2. Following Agreement of Written Scope | Redacted statements, chat exports, screenshots, notices, police report number | Verification of the party and acceptance of the scope, the fee structure, and the list of personnel authorized to access the records must occur. |
| 3. When Formal Filing Is Necessary | ID and address papers, proof of ownership, signed forms | A specific named recipient, a clearly stated objective, and a secure channel of communication are required for submission. Whenever feasible, transmit identity documents directly to the platform or authority requiring them. |
| At no stage, ever | Seed phrase, private key material, passwords, one-time codes, remote-access tools | No justification makes this safe. Any request of this kind is a red flag. |
Items you must never disclose
These items convey control rather than information. Any person who obtains them can move your funds or assume control of your accounts. No honest assessment, trace or filing requires them, so any request for one of them is a warning sign.
- Your seed phrase or recovery phrase, including any photograph of it.
- Keys to your wallet, whether stored as exported files or kept within a wallet application.
- Passwords and PINs used for wallets, exchanges, email accounts, banking and your phone.
- One-time codes, authenticator codes and backup codes.
- Remote control of your device, including any session where someone views or operates your screen.
- API keys that permit trading or withdrawals, together with complete card numbers and their security codes.
- A screenshot or scan showing any item above. Examine every image for an edge of the screen displaying a code or a phrase.
Redact before sending
Redaction means concealing details the next stage does not require, which limits the harm if a file is ever exposed. Carry out the concealment properly: a black box drawn over text in an editable PDF can leave the underlying text intact, and anyone is able to copy it out.
You may clear the text with an editing tool, print the page into a fresh PDF, or capture a screenshot of the redacted version and submit that file. Hidden file details should be removed as well, since photos and documents can carry metadata such as dates, device names and locations.
- Conceal ID numbers the request does not require, complete card numbers, transactions on a statement that are unrelated, and the names of individuals not involved in the case.
- Make sure your name, the relevant account or wallet identifiers, dates, amounts and the decisive lines remain visible.
- Mark the copy as redacted and retain the original without redactions. Never alter a number or a date.
- Place a visible note on copies of identity documents, for example the recipient's name and the date, so the copy becomes harder to reuse.
- Where a platform, police unit or court requests unredacted files, hand those files to that body directly wherever this is possible.
Choose a secure method for file submission
Send documents through the channel the party has named, and confirm that the channel details come from a source you trust. In practice this means typing their website address yourself rather than following a link from a message. Do not use social media chats, public group chats or open share links.
- When you can, use an upload portal on a site you reached yourself, or a channel that offers end-to-end encryption, such as email or messaging.
- When a shared folder link is involved, add an expiry date and a password, and disable any public access setting.
- Place your archive under a strong password, and transmit that password through a separate channel, for example a call you place yourself.
- Never send files from a device you suspect is infected, and avoid public Wi-Fi while submitting.
- Maintain a written record of each submission: what it contained, the date, the recipient and the method of transfer.
- Request in writing the duration the recipient retains your records and the method of deletion once the matter concludes.
How to confirm who you are dealing with
Verify the party before you submit anything beyond stage one. A genuine firm expects these checks and responds to them in writing. Our guide on spotting recovery scams contains a longer checklist, and it applies to us as well.
- The complete registered name, company number and official address, verified against the corporate register of the relevant country.
- Precisely who gains access to your papers: internal staff, independent lawyers, independent specialists. Request names and roles in the written scope.
- Whether any lawyer holds a licence, verified by you through the bar or legal register directly, never via a link supplied by them.
- Whether they reached out to you first. A cold contact following a loss is, as a rule, the most common warning sign.
- Whether they demand payment, access or secrets before stating in writing what they intend to do.
What a sound confidentiality commitment contains
Any provider can claim your data is protected. A fair undertaking is specific, set out in writing and candid about its limits. It states what is covered, who may view it, the purpose of its use, the retention period and how you can request deletion.
For our part, the written scope identifies who will see your documents, and each document is approved by you before submission. Request the same arrangement, in writing, from any provider.
| Item | What a fair promise states | What should raise concern |
|---|---|---|
| Scope of coverage | Every document and detail you submit, regardless of format | A commitment limited to 'sensitive' items, with no definition given |
| Who is permitted access | Identified staff and identified independent partners with a need to know, each bound in writing | 'Trusted third parties', unnamed and without stated roles |
| Purpose | Used solely to evaluate and manage your case | Applied to marketing, sale of data or files belonging to other clients |
| Storage and deletion | A declared retention period, plus deletion upon your request unless the law obliges the provider to retain the files | Missing retention policy, or deletion is refused |
| Disclosure | Passed to authorities only where the law compels it, with you informed where the law permits this | An assurance of total secrecy that no one is able to honour |
| Approval | You give approval for what each recipient receives | Documents sent on to others without your prior consent |
If you have already disclosed more than needed
This occurs to careful individuals, and there is a procedure for it. Follow the order set out below, and keep a written record of each step and its date. Should you want assistance organising the evidence afterwards, request our free assessment. We state in writing whether the matter is one we can take on, and we never request your secrets.
- Seed phrase or private key disclosed: regard the wallet as compromised. Create a new wallet on a clean device and transfer any remaining funds into it.
- Password or code disclosed: change the password immediately, terminate every active session and set up a new two-factor method.
- Remote access granted: disconnect the device, remove the tool, run a security scan and change your passwords from another device.
- Identity documents sent to an unverified party: notify your bank, ask what fraud alerts or credit monitoring exist in your jurisdiction, and monitor for accounts opened in your name.
- Report the incident to the police or the national cybercrime service, and record the reference number they issue.
Frequently asked questions
Is a passport required in order to receive a free assessment?
As a rule, no. A brief written account together with public information such as transaction hashes, wallet addresses and dates is sufficient for an initial view. Identity documents become relevant later, if a submission requires them, and in practice they are safer sent directly to the platform or authority making the request.
Is it safe to provide screenshots of my exchange account?
Yes, provided you inspect every image beforehand. Confirm it contains no one-time code, API key, recovery phrase or complete card number, and cover any detail the following step does not require. Retain the original screenshots, since a reviewer may request them later.
A service has asked to connect to my computer to examine my wallet. Should I permit this?
No. Granting remote access hands the other party control over your device, your accounts and whatever is visible on screen. A proper assessment, trace or filing does not require it. Regard the request as a scam and terminate contact.
For what period should a recovery service retain my documents?
No single rule exists, and in some jurisdictions the law sets retention periods. Request the period in writing, and ask how your files are destroyed once the case closes. A provider that cannot answer is not prepared to hold your data.
Can a provider promise that no other person will ever see my documents?
No honest provider can. It may need to share files with named lawyers or specialists to carry out the work, and the law can compel disclosure to authorities or courts. A fair promise states those limits and seeks your approval before files are sent anywhere.
How we can help
- Preparing digital evidence for crypto cases. Collect and file chats, screenshots and records so they can be used by the authority, the exchange or counsel.
- Support after a crypto scam. Structured support after a crypto scam: review, documentation, tracing and freeze requests.
- Recovering a wallet password or file. Forgotten password or damaged wallet file: screened independent specialists attempt recovery.
- Tracing stolen crypto and freeze requests. Tracing of stolen crypto, with freeze requests to exchanges and issuers and a police filing.
The content on this page is general in nature and is not legal advice.